


Cyber Security
One of the primary methods used by malware distributors to infect devices is by deceiving people into downloading and running malicious files, and to...
Hi, what are you looking for?
Texas investigators seek evidence of manslaughter, other crimes in 27 flood deaths at Camp Mystic
Maryland’s top court allows Democratic-backed congressional redistricting measure on November ballot
Missouri candidate wanted campaign manager to plant cocaine in opponent’s car, authorities say
Trump commutes sentence of convicted union leader John ‘Johnny Doc’ Dougherty, lawyer says
Idaho pushed anti-trans laws for years. Then a teen died.
Oil prices jump 5% after U.S. revokes Iran oil sanctions waiver following ship attacks
U.S. launches ‘major combat operations’ in Iran
Live updates: U.S. military begins ‘major combat operations in Iran,’ Trump says
Ryan Wedding, ex-Olympic snowboarder accused of being a drug kingpin, is arrested
The ICE officer who killed a Minnesota woman is a war veteran who spent over a decade working for DHS

Minnesota Names First Black Chief Justice Of State Supreme Court, Natalie Hudson
Local Governments Are Spending Billions Of Pandemic Relief Funds, But Some Report Few Specifics

Iran’s Foreign Minister Visits Saudi Arabia’s Powerful Crown Prince As Tensions Between Rivals Ease

In ‘BIdenomics,’ Congress Delivered A Once-In-Generation Investment — With Political Promise, Peril
Mishmash Of How Us Heat Deaths Are Counted Complicates Efforts To Keep People Safe As Earth Warms
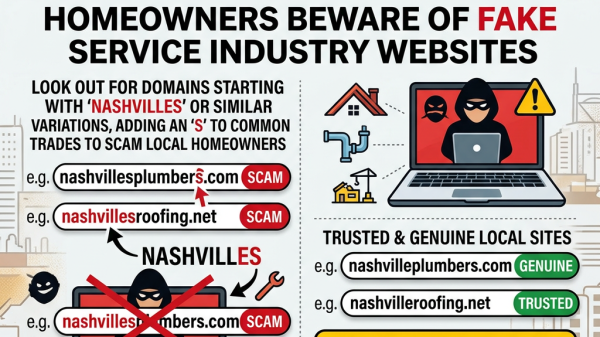
Nashville Homeowners are urged to use caution with scam of fake service industry websites taking over
CISA needs more money and less red tape, report says
CISA and HHS look to help the health sector ramp up cyber hygiene
Massive Phishing Attack Targeting 40+ Prominent Companies

Nation-state actors are exploiting AI for discord and attacks, DHS warns
Asian benchmarks mostly rise despite ongoing worries about Iran war
U.S. oil giant Chevron confirms it will expand operations in Venezuela
China’s economy grew at a 4.3% annual pace in the last quarter, slowest since late 2022
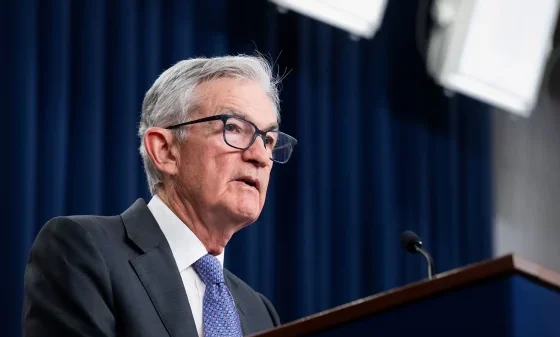
Federal Reserve likely to keep interest rates steady as Powell’s clash with the White House takes center stage
UPS to cut up to 30,000 more jobs in move away from low-profit Amazon shipments
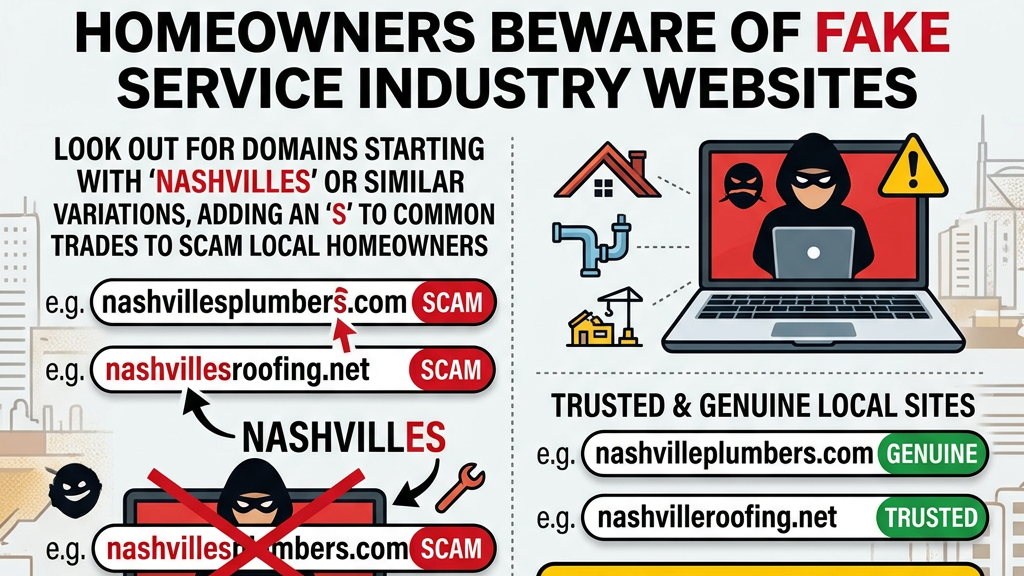
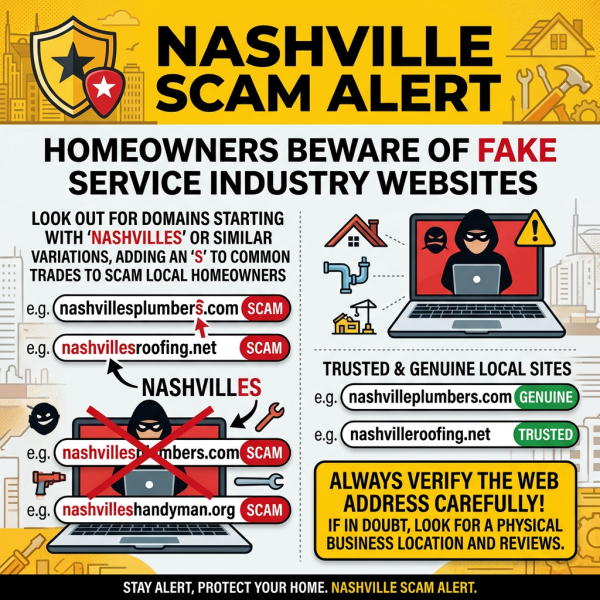
FOR IMMEDIATE RELEASE Consumer Alert: Network of Hundreds of Fake “Nashville” Home Service Websites Is Deceiving Local Homeowners Nashville, Tennessee — August 29, 2026...
Bureaucracy and dispersed authorities hinder the Cybersecurity and Infrastructure Security Agency’s ability to carry out its mission as network cyber lead, according to an...
Agency resources are intended to address the longstanding challenges health systems and hospitals have faced from increasingly advanced cyberattacks. The Cybersecurity and Infrastructure Security...
One of the primary methods used by malware distributors to infect devices is by deceiving people into downloading and running malicious files, and to...
From the infamous NotPetya campaign to the CCleaner backdoor, watershed infosec moments are not infrequent, but the SolarWinds supply chain attack stands out as particularly consequential. The so-called ‘Sunburst’...
A security vulnerability in file transfer software CompleteFTP allowed unauthenticated attackers to delete arbitrary files on affected installations. Developed by EnterpriseDT of Australia, CompleteFTP is a...


An Australian man was charged for developing and selling the Imminent Monitor remote access trojan, used to spy on victims’ devices remotely. A remote...


Researchers have uncovered a gigantic network of more than 11,000 domains used to promote numerous fake investment schemes to users in Europe. The platforms show...


Several adware apps promoted aggressively on Facebook as system cleaners and optimizers for Android devices are counting millions of installations on Google Play store. The...


A class action lawsuit has been filed in the Northern District of California against Meta (Facebook), the UCSF Medical Center, and the Dignity Health Medical...
Security researchers have identified multiple workflows in popular continuous integration and development (CI/CD) service GitHub Actions that are vulnerable to command execution. A research...


A pair of vulnerabilities in Google Cloud, DevSite, and Google Play could have allowed attackers to achieve cross-site scripting (XSS) attacks, opening the door...


Digital identity verification company Onfido has launched a new bug bounty program, in partnership with European vulnerability disclosure platform YesWeHack. The security rewards program will provide...

Recent Comments