


Cyber Security
Allan Friedman, the leader of a transparency initiative at the Commerce Department, is now at the Cybersecurity and Infrastructure Security Agency to realize the...
Hi, what are you looking for?
Texas investigators seek evidence of manslaughter, other crimes in 27 flood deaths at Camp Mystic
Maryland’s top court allows Democratic-backed congressional redistricting measure on November ballot
Missouri candidate wanted campaign manager to plant cocaine in opponent’s car, authorities say
Trump commutes sentence of convicted union leader John ‘Johnny Doc’ Dougherty, lawyer says
Idaho pushed anti-trans laws for years. Then a teen died.
Oil prices jump 5% after U.S. revokes Iran oil sanctions waiver following ship attacks
U.S. launches ‘major combat operations’ in Iran
Live updates: U.S. military begins ‘major combat operations in Iran,’ Trump says
Ryan Wedding, ex-Olympic snowboarder accused of being a drug kingpin, is arrested
The ICE officer who killed a Minnesota woman is a war veteran who spent over a decade working for DHS

Minnesota Names First Black Chief Justice Of State Supreme Court, Natalie Hudson
Local Governments Are Spending Billions Of Pandemic Relief Funds, But Some Report Few Specifics

Iran’s Foreign Minister Visits Saudi Arabia’s Powerful Crown Prince As Tensions Between Rivals Ease

In ‘BIdenomics,’ Congress Delivered A Once-In-Generation Investment — With Political Promise, Peril
Mishmash Of How Us Heat Deaths Are Counted Complicates Efforts To Keep People Safe As Earth Warms
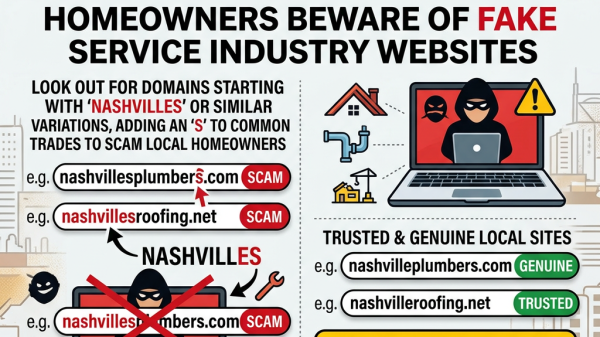
Nashville Homeowners are urged to use caution with scam of fake service industry websites taking over
CISA needs more money and less red tape, report says
CISA and HHS look to help the health sector ramp up cyber hygiene
Massive Phishing Attack Targeting 40+ Prominent Companies

Nation-state actors are exploiting AI for discord and attacks, DHS warns
Asian benchmarks mostly rise despite ongoing worries about Iran war
U.S. oil giant Chevron confirms it will expand operations in Venezuela
China’s economy grew at a 4.3% annual pace in the last quarter, slowest since late 2022
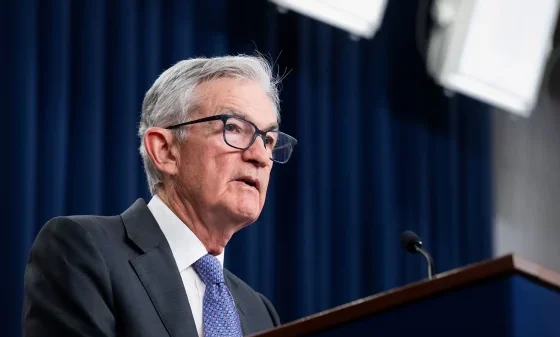
Federal Reserve likely to keep interest rates steady as Powell’s clash with the White House takes center stage
UPS to cut up to 30,000 more jobs in move away from low-profit Amazon shipments
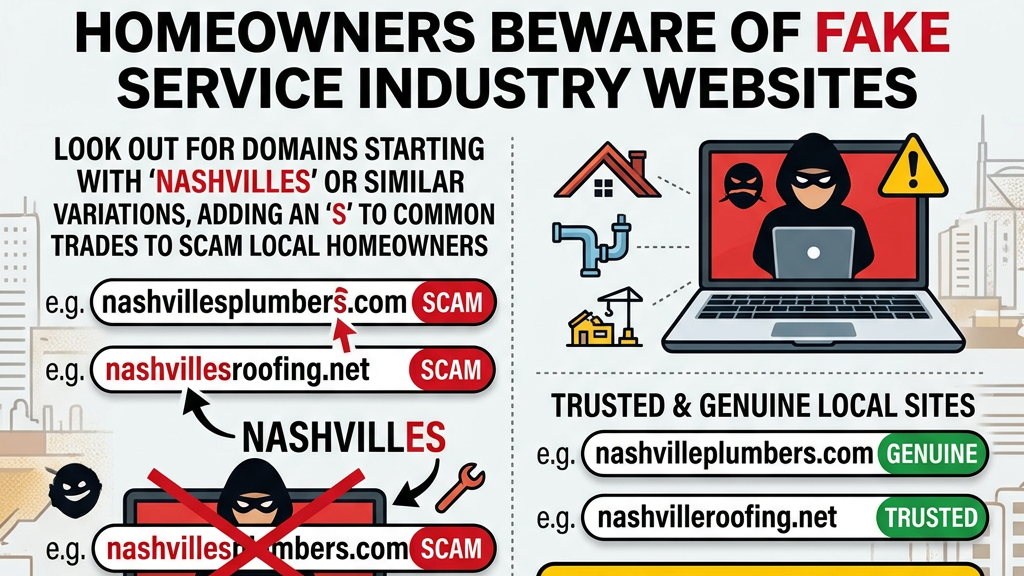
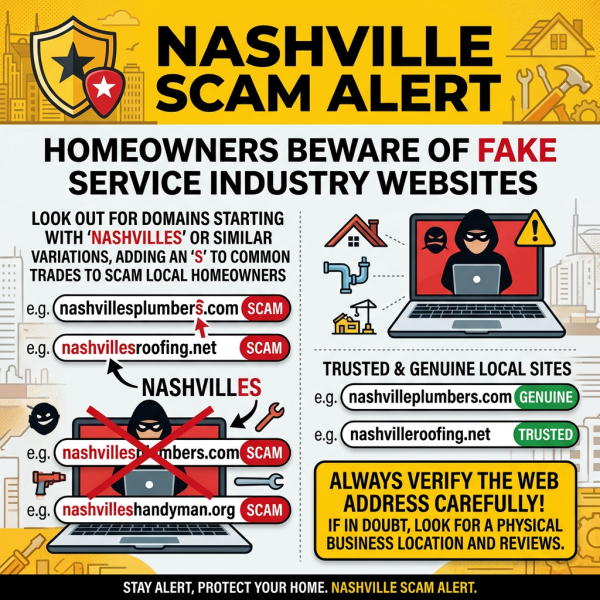
FOR IMMEDIATE RELEASE Consumer Alert: Network of Hundreds of Fake “Nashville” Home Service Websites Is Deceiving Local Homeowners Nashville, Tennessee — August 29, 2026...
Bureaucracy and dispersed authorities hinder the Cybersecurity and Infrastructure Security Agency’s ability to carry out its mission as network cyber lead, according to an...
Agency resources are intended to address the longstanding challenges health systems and hospitals have faced from increasingly advanced cyberattacks. The Cybersecurity and Infrastructure Security...
Allan Friedman, the leader of a transparency initiative at the Commerce Department, is now at the Cybersecurity and Infrastructure Security Agency to realize the...


A vulnerability in collaboration software is undergoing “mass exploitation,” according to U.S. Cyber Command. The Cybersecurity and Infrastructure Security Agency is imploring administrators to...


A critical vulnerability in a Cisco product designed to help service providers and enterprises deploy virtualized networks can allow unauthenticated actors to bypass authentication. The security...


Leader of a Pentagon-wide DevSecOps initiative, Nicolas Chaillan cited lack of support from senior leadership as one reason for his departure. Nicolas Chaillan—the Air...


The US Federal Trade Commission (FTC) has banned a spyware developer and its CEO from operating in the surveillance market in a landmark decision hailed by...


During congressional testimony, cybersecurity firm FireEye pushed for greater liability protections to be included in a draft cyber incident reporting bill. Rep. John Katko,...


Cybersecurity accreditation provider CREST has branded NCC Group “vicariously responsible” participants in a cheating scandal first reported last summer. In August 2020, CREST was...


The US Securities and Exchange Commission (SEC) has sanctioned multiple financial services firms for cybersecurity failures that led to the compromise of corporate email accounts and...


Microsoft has patched a fresh security vulnerability in Exchange Server that enables attackers to bypass authentication and snoop on employee emails. The high severity flaw...


The team behind TensorFlow, Google’s popular open source Python machine learning library, has revoked support for YAML due to an arbitrary code execution vulnerability. YAML is...

Recent Comments